News & Trends in the Cybersecurity Landscape
Cybersecurity Insights
More Tools Won’t Fix Your Security. A Plan Will.
More Tools Won’t Fix Your Security. A Plan Will.
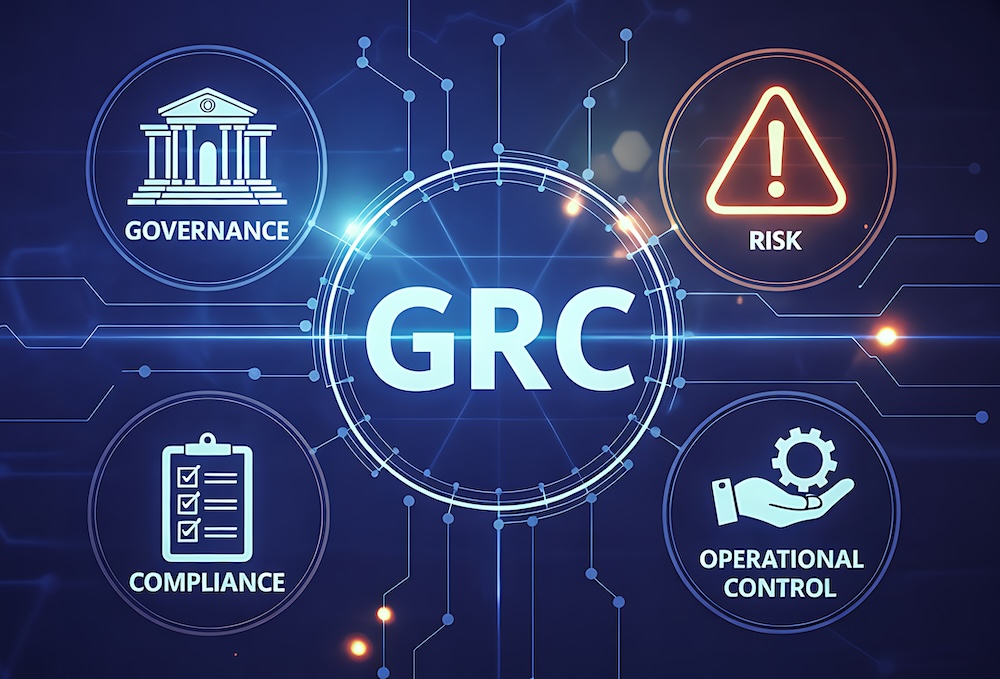
What Is Governance, Risk, and Compliance (GRC), and Why Is It Important?
What Is Governance, Risk, and Compliance (GRC), and Why Is It Important?
What Regulators Expect in 2026 and 2027
What Regulators Expect in 2026 and 2027
Top 5 Cybersecurity Vulnerabilities in Financial Institutions
Top 5 Cybersecurity Vulnerabilities in Financial Institutions
Why Nursing Homes Are Now Prime Targets for Cyberattacks
Why Nursing Homes Are Now Prime Targets for Cyberattacks
How Schools Should Prepare for Cyberattacks in 2026
How Schools Should Prepare for Cyberattacks in 2026
Ohio House Bill 96: What the New Cybersecurity Requirements Mean for Local Governments and Schools
Ohio House Bill 96: What the New Cybersecurity Requirements Mean for Local Governments and Schools
Vulnerability Scanning vs. Penetration Testing: What’s the Difference and Why It Matters